
PCI compliance for online stores doesn’t end with using a hosted checkout through Stripe or PayPal. Your hosting setup is still part of the transaction path, and if it’s not properly secured, it can put you out of compliance before the payment processor even sees the data.
If your hosting is in scope, things like outdated server software, weak TLS settings, loose access controls, or gaps in logging are enough to make you non-compliant.
Don’t worry though, I’m here to help.
In this guide, I’ll break down what PCI-compliant hosting actually means, why hosting matters more than most people think, and how to choose a setup that can handle real-world requirements.
I’ll also share my top five PCI-compliant hosting picks and explain why I recommend them.
Let’s start with the basics.
What PCI DSS actually is in simple words
PCI DSS stands for Payment Card Industry Data Security Standard. It’s a set of security requirements designed to protect credit card data from theft and misuse during and after an online transaction.
The PCI standard was created to reduce payment-related risks from things like stolen card numbers, compromised servers, and unauthorized access to sensitive systems. It’s managed by the PCI Security Standards Council, a group backed by major card networks including Visa, Mastercard, and American Express.
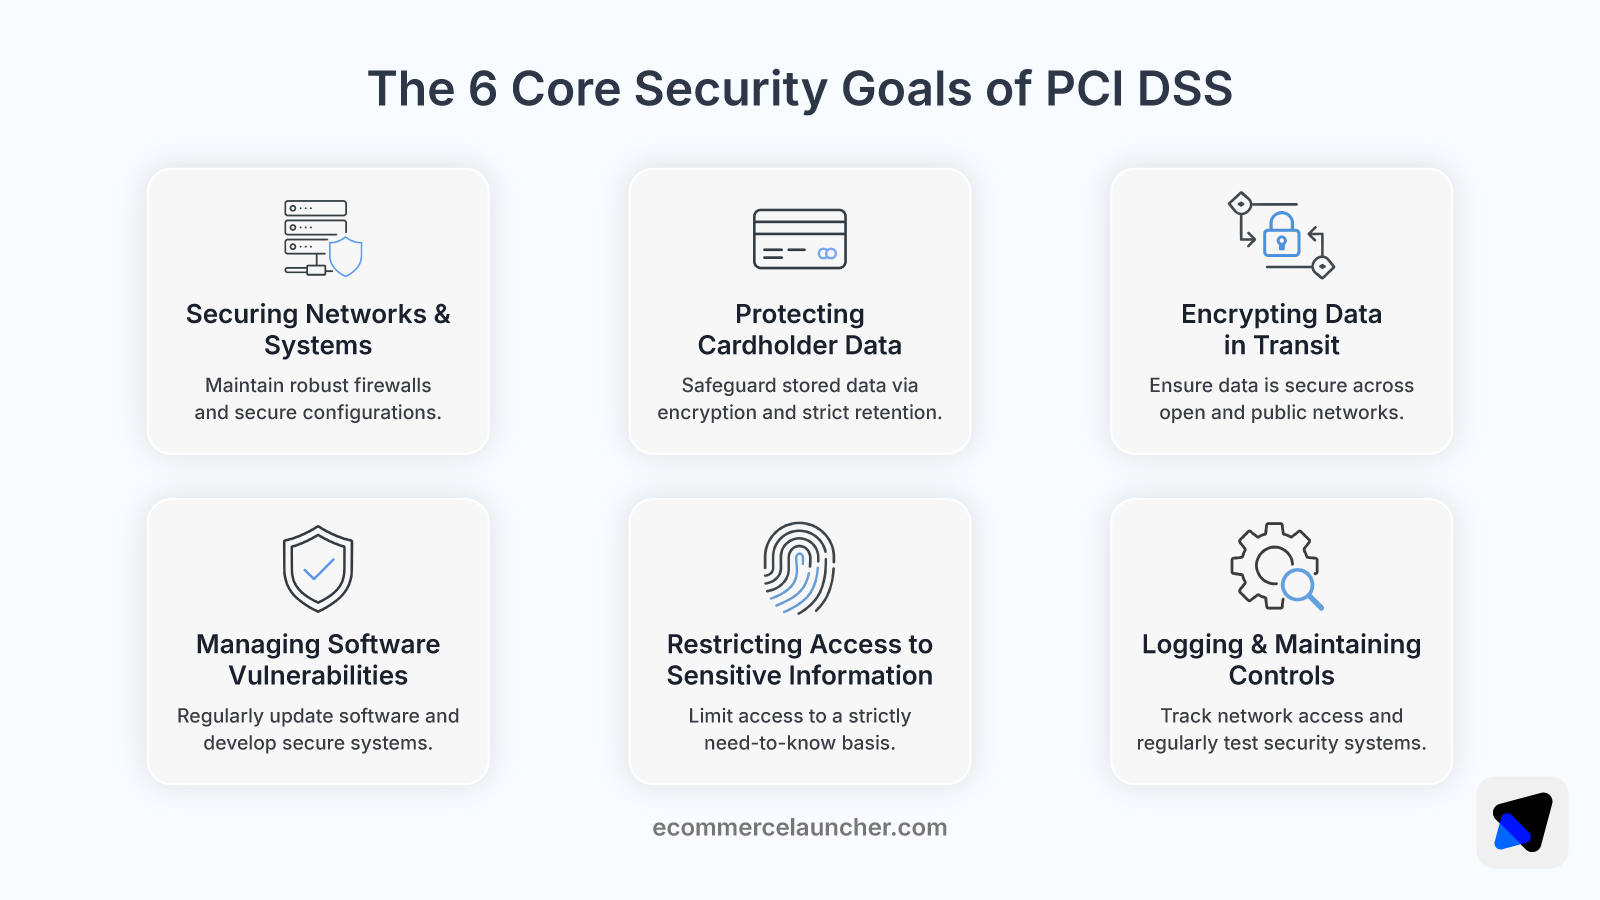
PCI DSS is organized into six security goals and twelve specific requirements. At a high level, they focus on:
- Securing networks and systems.
- Protecting stored cardholder data.
- Encrypting data in transit.
- Managing software vulnerabilities.
- Restricting access to sensitive information.
- Logging, testing, and maintaining controls.
Now, who does PCI DSS apply to?
PCI DSS applies to any business that stores, processes, or transmits cardholder data. That includes large retailers and small ecommerce stores. If your infrastructure handles card data in any way, even briefly, you fall under PCI scope.
Let’s understand what exactly counts as cardholder data first.
What counts as cardholder data according to PCI DSS
PCI DSS defines cardholder data very specifically. It’s not “anything related to a customer.” So, for example, a customer’s name or billing address doesn’t count on its own.
Instead, PCI DSS focuses on a narrow set of fields. If your systems see any of these, you’re in PCI scope.
Cardholder data includes:
- Primary Account Number (PAN): The credit card number.
- Cardholder name: The name printed on the card.
- Expiration date: The month and year the card expires.
- Service code: A three-digit code on the magnetic stripe that identifies usage restrictions.
These four items make up the core cardholder data set. The most important is PAN. It triggers PCI scope by itself. The others matter only if they appear with PAN.
How PCI DSS deals with CVVs and PINs
Not all card-related data is treated equally. Some details like the CVV code or the contents of a magnetic stripe fall under a separate category with stricter rules called Sensitive Authentication Data (SAD).
Sensitive authentication data is even more strictly protected than cardholder data. It includes:
- The full contents of the magnetic stripe or chip.
- CVV or CVC codes (the 3- or 4‑digit security code).
- PINs or PIN blocks.
You can collect SAD temporarily during payment authorization, but you’re not allowed to store them after that point. Storing it, even accidentally or in its encrypted form, is a violation.
In other words, while cardholder data can be stored under strict conditions, SAD must not be stored at all once the transaction is complete.
What actually triggers PCI scope
If your system handles full PAN in any form, including encrypted PAN, it is in PCI scope. It doesn’t matter whether you store it, forward it to a processor, or strip it out right away. Just handling it puts your environment under PCI rules.
Here’s a simple summary of when you are and are not in scope.
You are in PCI scope if:
- Your server collects a card number through a form.
- You decrypt or tokenize PAN in the browser.
- You log card data by mistake.
- You forward card details to a processor through your backend.
You are not in scope if:
- PAN never enters your systems at all.
- You use a fully hosted checkout page from a gateway.
- Card data is collected and submitted directly using gateway-provided scripts.
Seeing the PAN is enough to bring everything into scope. The other fields (name, expiry, service code) only matter when combined with PAN. If PAN is present, the others inherit the same level of protection.
If PAN never enters your systems and your server cannot affect the payment form or the scripts that handle card data, your server stays out of PCI scope.
PCI DSS Levels explained
PCI DSS applies to any business that stores, processes, or transmits cardholder data. That includes large retailers and small online stores. If your infrastructure handles card data in any way, even briefly, you fall under PCI scope.
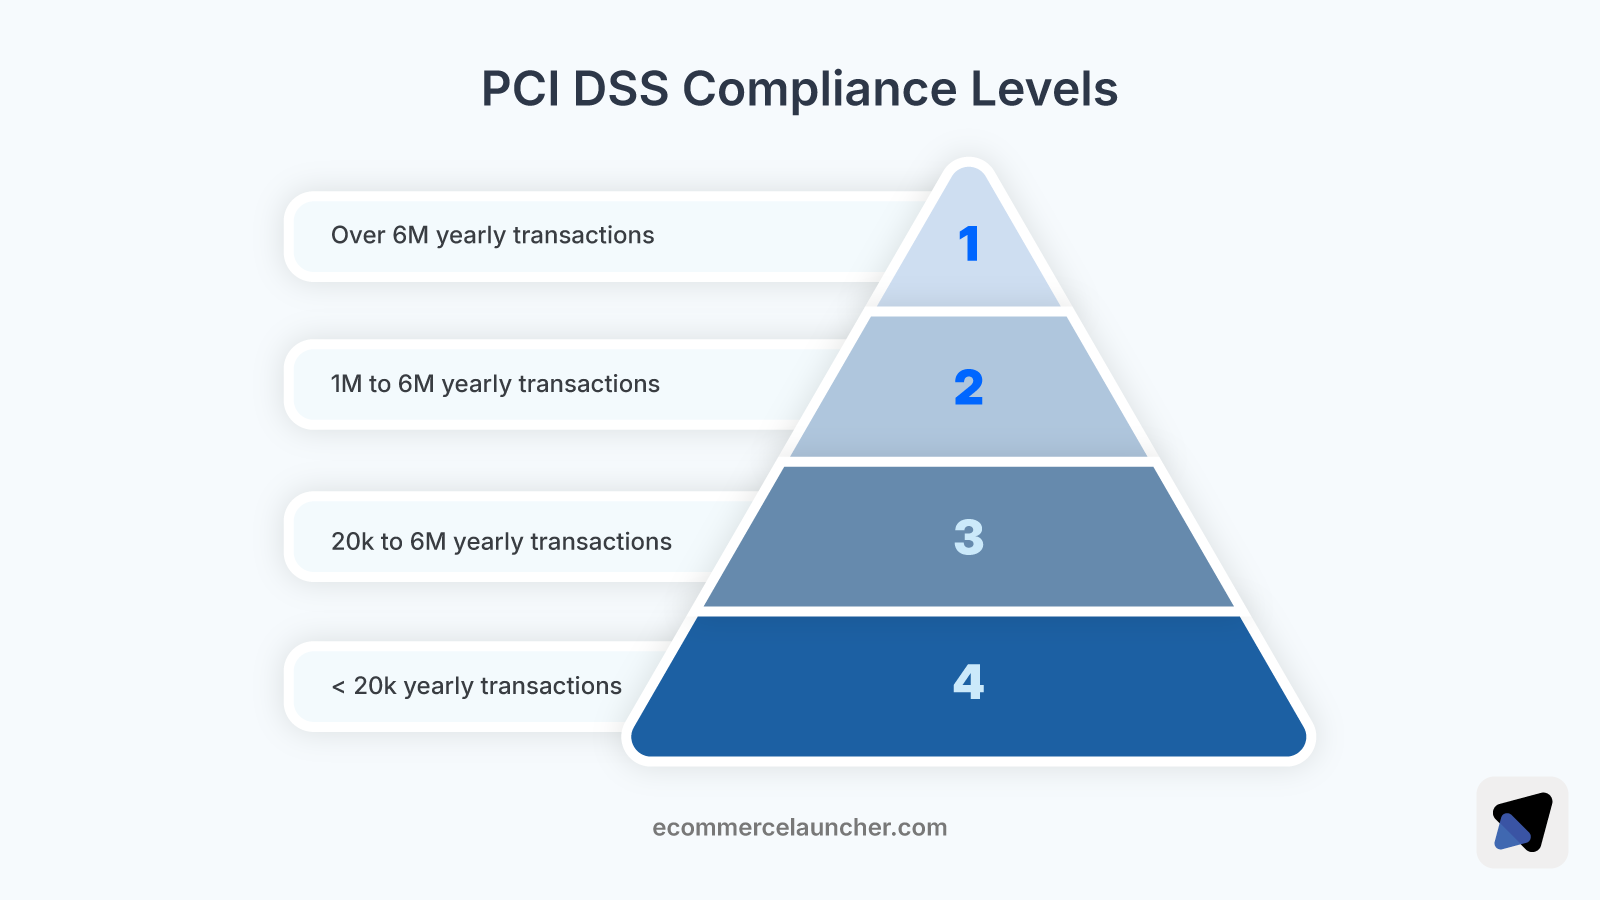
Depending on how many transactions you process per year, you fall into one of four PCI levels. These levels don’t change the core requirements but they do affect how you prove compliance.
- Level 1: Over 6 million transactions per year. Requires a formal audit by a Qualified Security Assessor (QSA).
- Level 2: 1 to 6 million transactions. May need a self-assessment or third-party validation.
- Level 3: 20,000 to 1 million eCommerce transactions. Typically uses self-assessment (SAQ).
- Level 4: Fewer than 20,000 eCommerce transactions or 1 million in-person. Also uses self-assessment, but may face more scrutiny from payment providers.
PCI DSS levels are assigned by the payment brands or your acquiring bank. They determine what kind of validation you need, not whether PCI applies at all.
Now that we’ve covered what falls under PCI scope and who it applies to, let’s talk about what PCI-compliant hosting actually means and when you need it.
What PCI-compliant hosting actually means
PCI-compliant hosting is a server setup that meets the technical and security requirements of the PCI DSS standard. If your infrastructure handles credit card data in any way, it’s considered part of the cardholder data environment, and your hosting provider becomes a key part of your compliance.
A PCI-compliant hosting environment must include secure configurations, strong firewall rules, properly encrypted connections, access restrictions, and reliable logging. If your host doesn’t support them, your compliance breaks before anything reaches the payment processor.
Shared hosting environments rarely qualify as PCI compliant. When multiple sites run on the same server with no isolation, one weak site can expose everyone else. That setup introduces too much risk and typically fails PCI requirements.
Environments like dedicated hosting for ecommerce, private cloud setups, or well-configured VPS instances, give you better isolation and security. But infrastructure alone isn’t enough.
You’re responsible for making sure the environment stays secure, whether you handle it yourself or rely on a provider to manage it. That includes patching, access control, and basic system hygiene.
Even if you have a managed hosting provider, the responsibility to ensure PCI compliance isn’t fully theirs. Your application, your plugins, your code, and your integrations still matter.
PCI compliance is a shared responsibility, and your hosting provider can’t cover for poor choices in your stack.
Hosting is just one layer of PCI compliance. But if that layer isn’t secure, nothing else will hold.
How PCI DSS 4.0 changes hosting requirements
PCI DSS 4.0 raises the baseline for compliance. It introduces tighter rules for access control, continuous monitoring, and system isolation, especially in environments that handle cardholder data.
The update was released in March 2022, with full enforcement starting in March 2025. If your hosting provider hasn’t adapted yet, there’s a risk your setup is already falling short.
For hosting providers, PCI DSS 4.0 brings three major changes:
- Stronger access control. Multi-factor authentication is now required for all access to systems in the cardholder data environment, not just remote access. Password requirements have also been made stricter.
- Continuous monitoring. Hosting environments must have active logging, alerting, and response procedures. That includes tracking failed logins, unusual admin activity, and unauthorized changes to system files.
- Documented segmentation. If your hosting setup includes systems that handle cardholder data, and your host claims those systems are isolated, they need to prove it. That means written firewall rules, tested access boundaries, and supporting evidence.
If you’re a merchant, this doesn’t mean you have to manage those controls, but you do need to confirm they exist. You can do that by asking your hosting provider to show you how they meet the requirements, how they document controls, and how they support your own compliance.
The new version doesn’t just check whether controls exist. It also looks at whether they work over time. That shift from static to continuous enforcement is one of the biggest changes in PCI DSS 4.0, and your hosting setup needs to reflect it.
When you do (and don’t) need PCI-compliant hosting
Whether you need PCI-compliant hosting depends entirely on how your store handles credit card data. Here’s how to make that call based on your checkout setup.
1. Gateway-hosted checkout
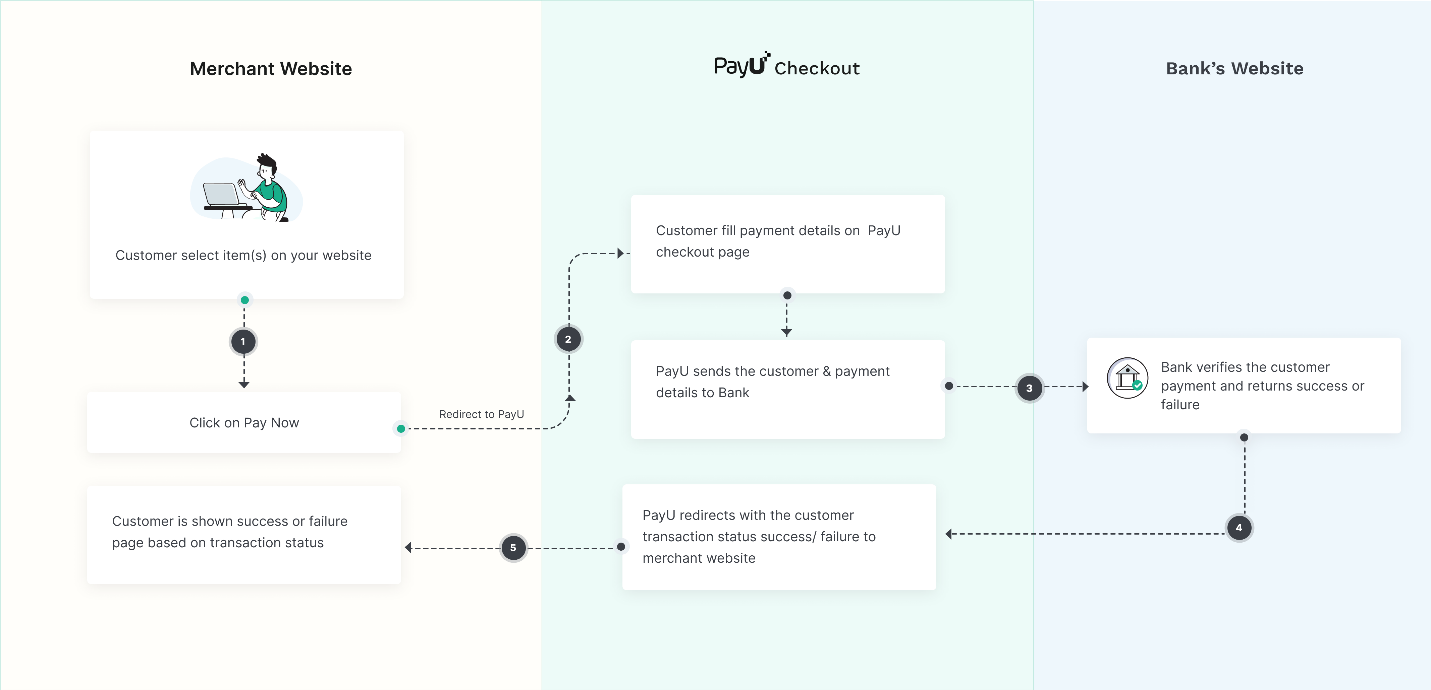
Image Source: PayU
If you use a fully hosted payment gateway like Stripe Checkout, PayPal Payments Standard, or Square’s offsite checkout, and no part of your site touches cardholder data, your hosting setup stays out of PCI scope.
In this model:
- Cardholder data never enters your systems.
- Checkout is handled entirely on the provider’s domain.
- Your integration uses a redirect or iframe that you don’t control.
Now that doesn’t mean you’re fully off the hook. Even though your hosting environment is out of PCI scope, you’re still responsible for general website security (TLS, patching, malware scanning).
If this describes your setup, you typically qualify to use SAQ A, the simplest PCI self-assessment form.
2. Embedded fields or tokenization
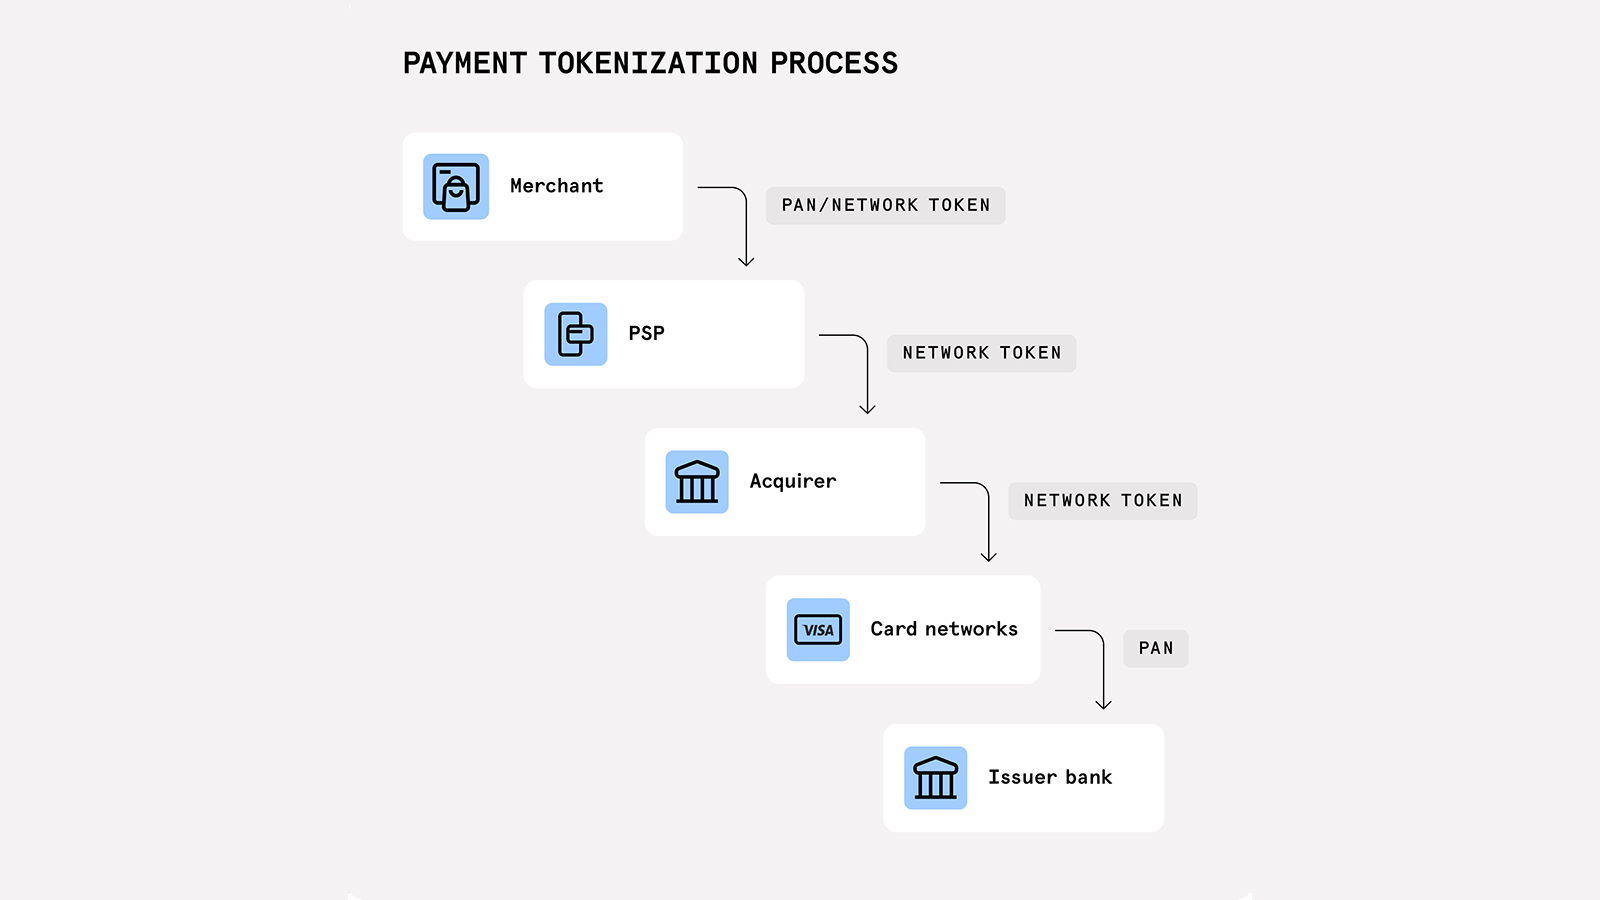
Image Source: Checkout.com
If you embed provider-hosted fields into your own checkout page, such as Stripe Elements, Braintree Hosted Fields, or similar solutions, cardholder data never hits your server, but your site still helps collect it.
In this model:
- Card fields are hosted and served by the payment provider.
- Your page hosts the fields, but the provider’s script submits the card data.
- JavaScript runs on your domain and plays a role in data collection.
Because your page hosts the scripts that render and control the payment fields, your hosting environment becomes partially in scope.
Even if the card data doesn’t touch your server, the integrity of your site matters. A compromised site could modify those fields and capture data before it leaves the browser.
In this case, PCI DSS assigns you to SAQ A-EP, a mid-level PCI category. Your hosting environment doesn’t need to meet every PCI control, but it must still be secured, segmented, and monitored.
And the SAQ A-EP form requires you to meet additional hosting-related requirements, including:
- Securing and hardening your web server
- Keeping software up to date
- Restricting admin access
- Monitoring and logging activity
So even though the card data never reaches your server, the environment must be trustworthy. Your hosting provider must support the SAQ A-EP outlined controls, and you’re responsible for verifying that they’re in place.
3. Custom or self-hosted checkout
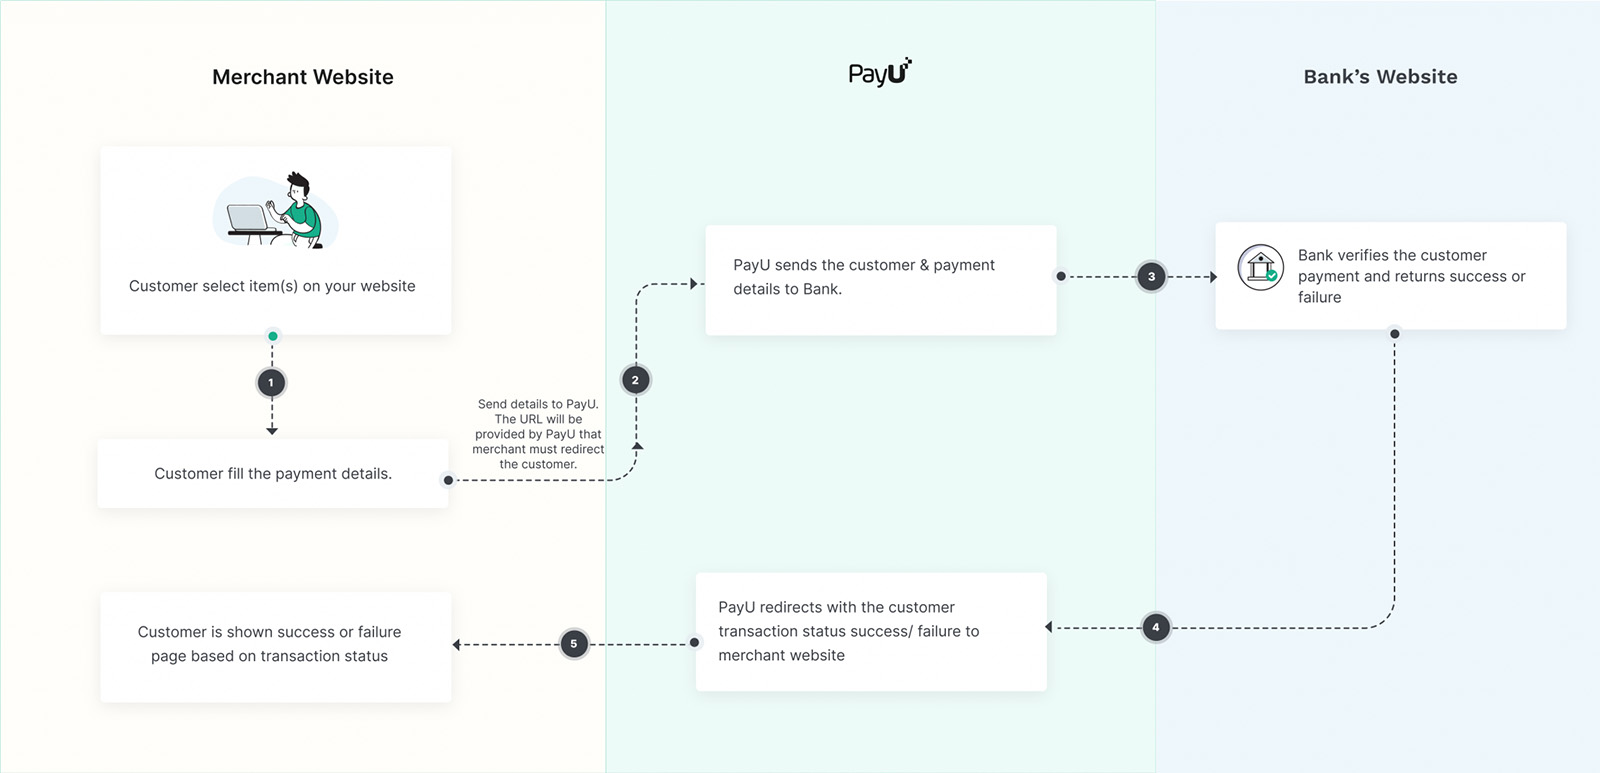
Image Source: PayU
If your store collects, stores, processes, or forwards cardholder data, whether through a custom form, plugin, or backend process, your hosting is fully in PCI scope.
Common signs you’re in this category include:
- Your checkout form posts to your own server.
- You handle encryption, tokenization, or forwarding on your backend.
- You use a payment plugin that sends card data through your server rather than directly to the gateway.
Once your infrastructure touches card data in any way, it becomes part of what PCI calls the cardholder data environment. That means your hosting setup must meet the full PCI DSS requirements, including network segmentation, access control, vulnerability management, and real-time monitoring.
This falls under SAQ D, which carries the full weight of PCI compliance. Your hosting provider must support strong access controls, system hardening, network segmentation, and continuous monitoring. You’re also responsible for making sure those measures are in place and working.
Still confused?
Ask yourself this question: Does any part of your online store infrastructure, including your application or server, interact with cardholder data?
If the answer is Yes, then you need PCI-compliant hosting.
The risks of using shared or non-compliant hosting
Shared hosting often lacks the strong segmentation needed to isolate cardholder data environments.
When multiple customers share the same server, including the file system, memory, or logging, one mistake or compromise can affect everyone else. That kind of environment can’t guarantee isolation, and without isolation, there’s no real compliance.
That isn’t just theoretical.
One study showed that attackers with access to a single shared-hosting account could read log files from other sites on the same server. Looking at over 440,000 domains across 1,200 shared hosts, they found that providers with weaker infrastructure controls saw significantly higher rates of phishing and malware.
Shared cPanel environments are especially risky. They often allow shell access, cron jobs, and scripts with overly broad permissions. A misconfigured cron job or a world-writable folder in one account can open the door to every other tenant.
Some shared hosts claim they isolate customers at the software level. But PCI DSS doesn’t allow “best effort” segmentation. It expects hard boundaries. No shared logs, no shared temp directories, and no paths for data to leak between accounts. Shared hosting can’t meet that bar in most cases.
If your environment isn’t fully isolated, PCI considers it part of the same cardholder data environment. That means someone else’s bad plugin or outdated software could drag your store out of compliance. The worst part is that you might never see it coming.
5 things a PCI-compliant host must provide
A PCI-compliant hosting provider must enforce strict security controls that protect cardholder data, limit who can access your systems, and detect threats quickly.
Here’s a breakdown of what a hosting environment needs to provide to support PCI DSS in a real, operational sense.
1. Network and Infrastructure Controls
Your hosting environment must protect cardholder data by isolating it from untrusted systems and keeping the attack surface small. Firewalls need to control traffic between network zones, and proper segmentation should block any system that doesn’t need access to card data.
Your host also needs intrusion detection or prevention to catch scans, exploit attempts, and other suspicious activity. PCI DSS requires monitoring and alerting mechanisms that detect suspicious activity promptly.
All services should run with secure defaults. Unused ports and services should be disabled, secure protocols enforced, and patches applied on a set schedule. High-severity issues should be fixed quickly.
2. Encryption and Data Protection
Protecting cardholder data requires strong encryption in transit and, when needed, at rest. All data sent over the network must use secure TLS protocols, at least TLS 1.2, and your hosting environment should enforce this across every service.
If cardholder data is stored at all, it must be encrypted with industry-standard algorithms such as AES-256. The host should provide reliable encryption for disk volumes or file storage.
PCI DSS expects controlled access, secure storage, and regular rotation of cryptographic keys. Your host should either supply the tools to manage keys safely or define how they handle that responsibility.
3. Access Control
PCI DSS limits who can access systems and how they do it, so the hosting environment has to support strict controls. Users and services should only get the access they need, and the host should offer fine-grained permissions and roles to keep movement inside the environment tight.
Any administrative access to systems that handle card data must use MFA, whether it’s console, SSH, or a control panel. PCI DSS 4.0 applies this to all admin access, not just remote sessions.
Every account must be tied to a specific person, with full logging for each access path. Shared credentials aren’t allowed, so the host needs to support named accounts with clear audit trails.
4. Logging and Monitoring
PCI DSS requires continuous monitoring, not just secure systems. Logs need to be complete, hard to tamper with, and detailed enough to reveal threats. Your host should record access attempts, configuration changes, software installs, privilege escalations, and system alerts. These logs matter when something goes wrong.
Logs also have to be kept for at least a year, with three months ready for quick access. The hosting platform should support that retention period or give you the tools to meet it.
Scattered logs make it easy to miss issues, so you need a central place to collect and review them. Whether the host provides this directly or through integrations like syslog, SIEM tools, or external storage, the setup has to support centralized logging.
5. Physical and Cloud Infrastructure Security
Your provider should be able to show that the underlying infrastructure is secure, whether you use physical servers or cloud platforms.
For data centers, PCI DSS requires strong physical controls, including badge systems, surveillance, staffed entry points, and visitor logs. The provider should use facilities that meet these standards and be able to show proof.
If you use AWS, GCP, or Azure, the cloud vendor handles physical security, but your host still has to explain how they rely on those services and how they keep your virtual systems segmented and protected.
Across all setups, PCI DSS expects clear responsibility boundaries. Your provider should give you a responsibility matrix that spells out what they handle and what you are supposed to manage.
The 3 best PCI-compliant hosting providers for ecommerce
Here are the three PCI compliant hosting providers I recommend for ecommerce store owners. Each of these has unique strengths that earn them a place on this list.
1. Atlantic.Net

Atlantic.Net is a leading USA-based bare metal and dedicated hosting provider that has been in business since 1994. It provides hosting environments that support PCI DSS requirements, including cloud, VPS, and dedicated options designed for service providers and merchants that need strict security controls.
As a PCI compliant host, Atlantic.Net maintains SOC 2 and SOC 3 audit reports for its infrastructure. Their PCI environments include managed firewalls, intrusion detection and prevention, encrypted backups, and secure VPN access.
What I like about the PCI-ready hosting from Atlantic.Net is that it lets you deploy isolated, audit-ready systems designed to meet PCI DSS technical requirements. The best part: it’s backed by a team that understands assessor expectations and compliance documentation.
Atlantic.Net provides a tightly managed hosting stack with clear control boundaries and pre-configured security layers. They’re one of the few providers that offer infrastructure features like custom network segmentation, which can help you work toward scope reduction.
Key features:
- SOC 2 / SOC 3 audited infrastructure.
- Managed firewalls, IDS/IPS, MFA, and VPN included.
- Encrypted storage and daily offsite backups.
- Support for cloud, dedicated, or hybrid PCI environments.
- Access to compliance-trained support staff and documentation assistance.
Best PCI-compliant hosting provider for: B2B platforms or service providers building multi-client environments that must isolate and secure cardholder data under SAQ-D or full audit conditions.
Pricing: Atlantic.Net’s PCI-compliant hosting starts around $416/month for fully managed PCI hosting. Final cost depends on environment scope and service level.
2. Liquid Web
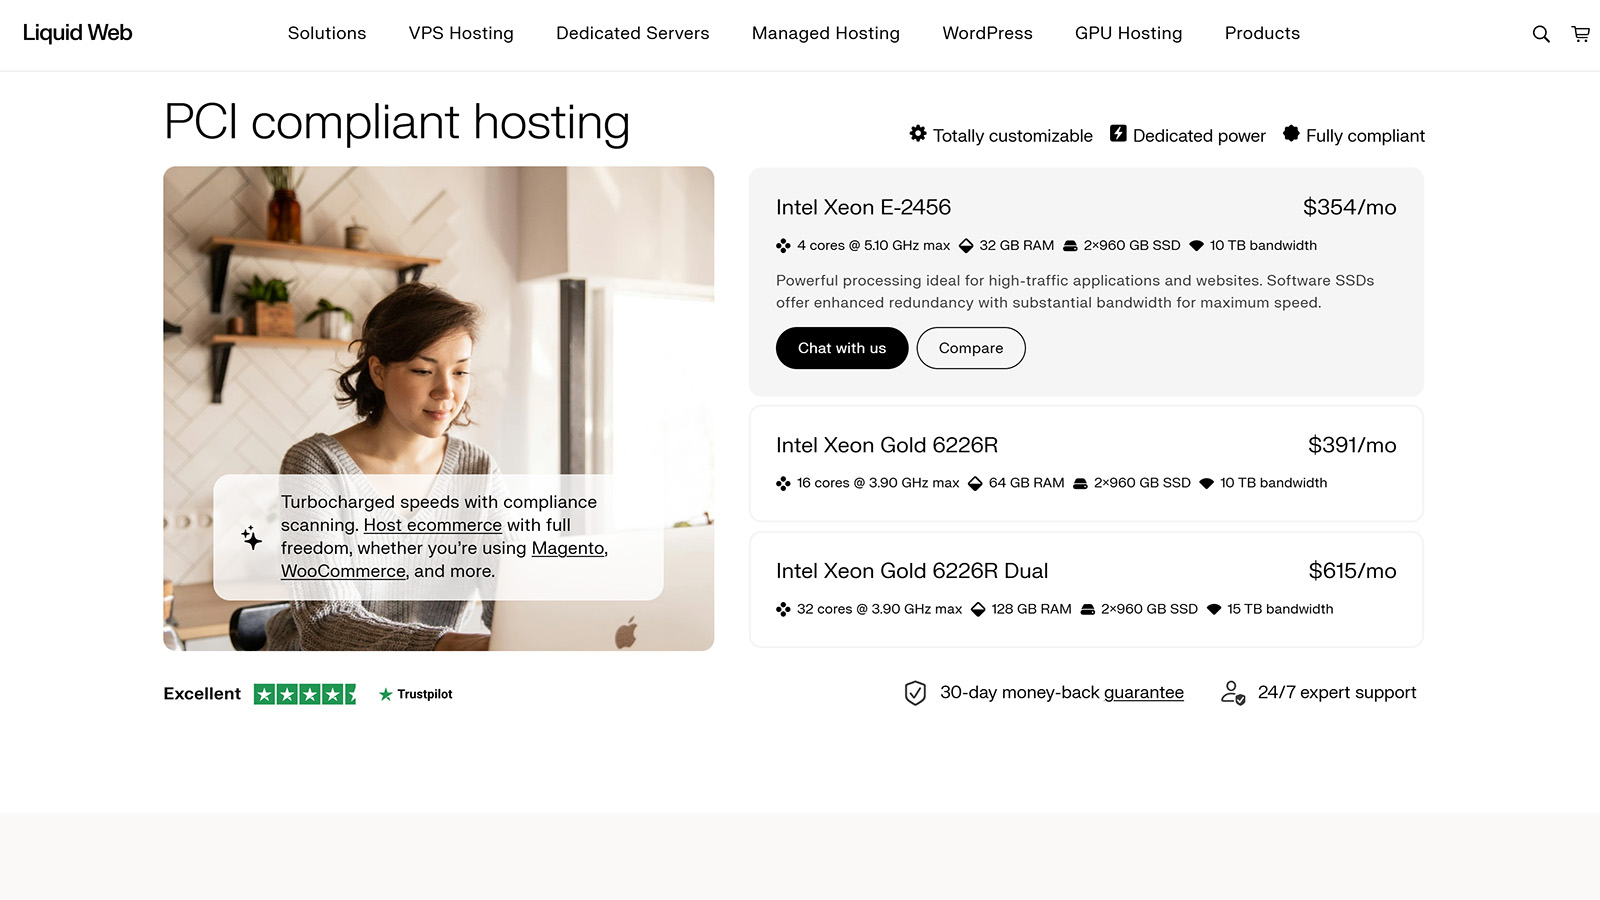
Liquid Web provides PCI-compliant hosting on managed VPS, cloud, and dedicated servers, designed for businesses that process payments at scale. They are a PCI-DSS Level 1 provider that offer key controls like network segmentation, vulnerability scanning, secure backups, and 24/7 support from compliance-trained staff.
What I like about Liquid Web is that they have dedicated environments with ongoing scan remediation and support built in. They support full backup and disaster‑recovery via Acronis Cyber Backups, giving you off-server, encrypted backups, full‑server and file‑level restores, and ransomware protection.
What makes Liquid Web stand out is their focus on higher-traffic ecommerce and SaaS platforms that need both performance and compliance.
I’ve tested their bare metal servers and I can confidently say that they’re one of those rare providers that offer the perfect balance of performance, security, and high quality support.
Key features:
- Level 1 service provider with built-in scan tools and audit support.
- Managed firewalls, DDoS protection, SSL, and isolated environments.
- Quarterly PCI scans with remediation for up to 10 IPs.
- Off-server encrypted backups and secure data handling.
- Support staff available 24/7/365.
Best PCI-compliant hosting provider for: High-volume ecommerce stores that need audit-ready hosting, strong uptime, and direct support for PCI remediation.
Pricing: Liquid Web’s PCI-compliant hosting starts at $354/month for an Intel Xeon E‑2456 setup with 4 cores, 32 GB RAM, 2×960 GB SSD, 10 TB bandwidth.
3. Verpex
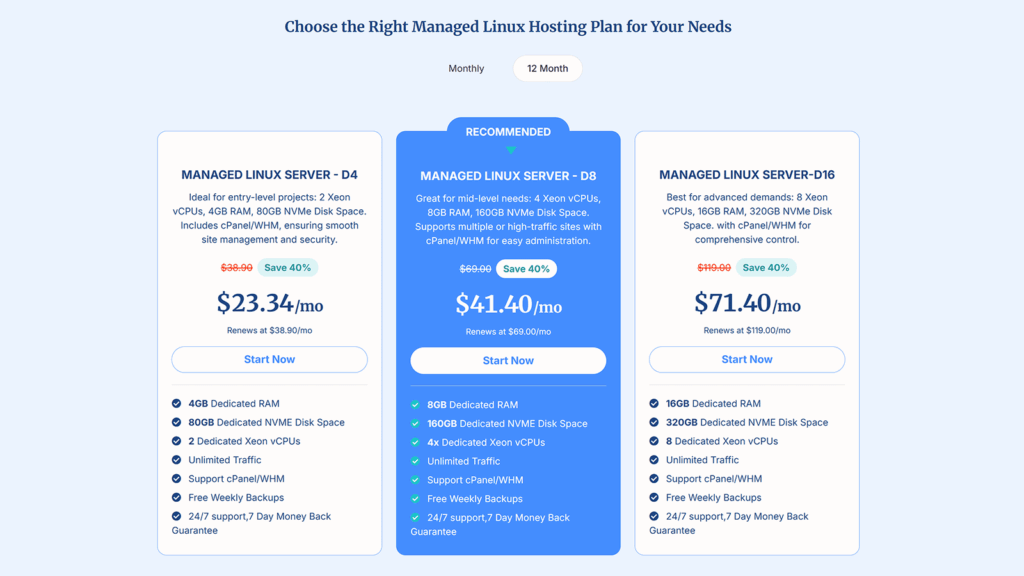
Verpex offers managed cloud and VPS hosting that can be configured for PCI compliance, but it’s not a turnkey solution. You get free SSL, customizable firewalls, daily backups, and 24/7 support, all of which help cover the basics.
Verpex promotes their managed cloud servers as “PCI Compliant,” but you’re expected to handle the actual compliance work. While Verpex will assist you with achieving compliance, there’s no mention of PCI-specific certification or audit-ready features, so it’s more of a flexible base than a complete solution.
That said, for smaller businesses or teams with technical know-how, Verpex is the most cost-effective way to meet PCI requirements without jumping straight to enterprise hosting. If you’re someone who needs a PCI compliant host on a budget, Verpex is the way to go.
Key features:
- Managed cloud and VPS plans with customizable firewall settings.
- Free SSL, daily backups, malware scanning, and monitoring.
- 24/7 support for server management and troubleshooting.
- SSD storage and strong baseline performance across plans.
- Lower cost than most managed PCI hosting providers.
Best PCI-compliant hosting provider for: Small ecommerce stores or early-stage businesses on a budget that want full control over setup and are comfortable managing their own compliance.
Pricing: Verpex managed cloud plans start at $23.34/month, with higher tiers available depending on resources and configuration needs.
Not all PCI-compliant hosts are equal, here’s what really matters
We’ve covered everything you need to know about PCI-compliant hosting for ecommerce. I explained what PCI DSS is, what PCI-compliant hosting is, when you need PCI hosting, and shared my top 3 PCI hosting provider recommendations for different use cases.
PCI compliance is mandatory when you’re processing payments on your website. But not every provider handles it the same way. Some give you an audit-ready setup with hands-on support while others give you the tools but expect you to manage compliance on your own.
Atlantic.Net and Liquid Web are great options if you want infrastructure that’s designed for PCI compliance from the ground up. Verpex is a lot cheaper but requires more effort on your side to meet the standard.
No matter which provider you choose, make sure you understand where their responsibility ends and yours begins. And if you have any more questions, get in touch with me. I’m here to help!
