
Hosting healthcare data isn’t just a tech decision—it’s a compliance one. Even with secure apps and trained staff, one misstep in your hosting setup can trigger a HIPAA violation.
No BAA? Weak encryption? Poor access logs? That’s all it takes to make your business non-compliant.
Don’t worry though, I’m here to help.
In this guide, I’ll break down what HIPAA-compliant hosting involves, why it matters, and how to choose a provider that’s secure, scalable, and ready for audit—no matter your size.
Let’s start with the basics.
What Is HIPAA-Compliant Hosting?
HIPAA-compliant hosting refers to infrastructure that meets these federal requirements—not just in technology, but in policies, procedures, and legal accountability.
Under the Health Insurance Portability and Accountability Act (HIPAA), any entity that stores or processes electronic protected health information (ePHI) is required to follow specific security, privacy, and breach notification standards outlined in the HIPAA Security Rule and Privacy Rule, with additional enforcement and breach notification requirements under the HITECH Act.
Hosting healthcare data comes with legal obligations that go far beyond general cybersecurity. If your hosting provider doesn’t fully support HIPAA compliance, your organization may be exposed to penalties, data loss, and liability in the event of a breach.
Let’s go over what makes a hosting environment compliant—and what separates a good provider from a risky one.
Key Safeguards Required by the HIPAA Security Rule
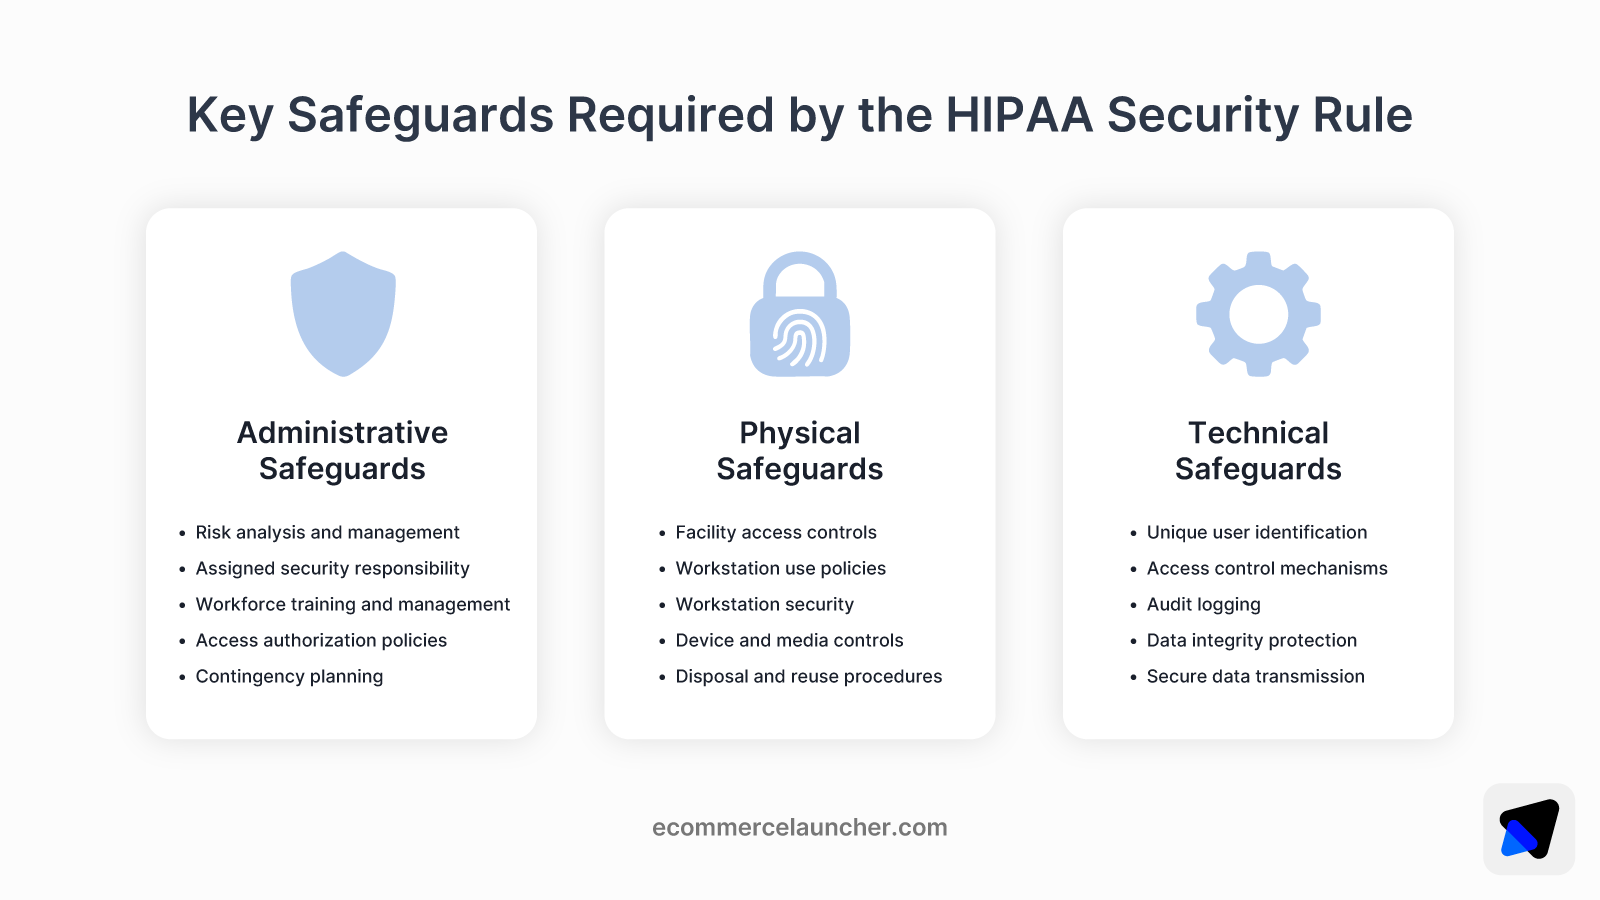
The HIPAA Security Rule (45 CFR Part 160 and Subparts A and C of Part 164) defines three categories of safeguards that must be enforced across any system that handles ePHI:
1. Administrative Safeguards (45 CFR §164.308)
These are the foundational policies and procedures that govern who can access data, how they’re trained, and how risks are managed over time. A hosting provider must support:
- Workforce training and role-based access: Ensure staff only access systems necessary for their job function.
- Security incident procedures: Defined plans to detect, respond to, and document security events.
- Ongoing risk assessments: Regular evaluations of system vulnerabilities and threat exposure.
While some of these responsibilities fall on the healthcare entity, your host must provide tools and documentation to support access controls and incident response tracking.
2. Physical Safeguards (45 CFR §164.310)
These controls protect the hardware and data center environment where ePHI is stored. A HIPAA-compliant host should offer:
- Restricted physical access to servers: Biometric locks, video monitoring, and on-site security.
- Environmental protection: Redundant HVAC, fire suppression, and backup power.
- Device and media controls: Policies for data disposal and reuse of drives that may contain PHI.
Verify that your provider uses Tier III or IV data centers with controlled facility access and documented destruction policies for physical media. Those facilities often meet or exceed the physical safeguard standards outlined in the Security Rule.
3. Technical Safeguards (45 CFR §164.312)
These define how ePHI is protected at the software and network level. Your hosting provider must enforce:
- Encryption: End-to-end encryption using AES-256 for data at rest, and TLS 1.2+ for data in transit.
- Audit controls: System-wide logging of access, changes, and unauthorized attempts, available to you during an audit or investigation.
- Integrity controls: Mechanisms to confirm data hasn’t been altered or destroyed without authorization.
- Access control mechanisms: Including multi-factor authentication (MFA), role-based permissions, and automatic session timeouts.
Look for hosts that offer logging dashboards, access management tools, and automatic log retention (at least six years is recommended for HIPAA alignment).
Why a Signed Business Associate Agreement Is Mandatory
Under HIPAA’s Administrative Safeguards (45 CFR §164.308(b)(1)), covered entities must enter into a Business Associate Agreement (BAA) with any vendor that stores or processes ePHI on their behalf.
The contract:
- Transfers specific security and privacy obligations to your hosting provider.
- Defines who is responsible for breach notification and investigation.
- Legally binds the provider to use proper safeguards and report any violations.
It’s not enough for a provider to say they “support HIPAA.” If they won’t sign a BAA—or only sign a watered-down version—you may be held liable for a breach, even if the root cause was their infrastructure.
That’s because, while covered entities are generally not liable for the actions of their business associates, they can be held responsible if they fail to act upon knowledge of a pattern of activity or practice by the business associate that constitutes a material breach or violation of the BAA.
That’s why, you should ensure your hosting BAA should:
- Specify the scope of services covered.
- Define roles in audit response and data incident handling.
- Include language about subcontractor responsibilities, if applicable.
Remember: The BAA is the legal backbone of HIPAA compliance for third-party services. Without it, you’re exposed—even if the system is technically secure.
Key Technical Requirements for HIPAA Hosting
A signed BAA is a legal foundation—but it’s the technical safeguards that enforce compliance day to day. These systems are what ensure that ePHI remains secure, accessible, and intact.
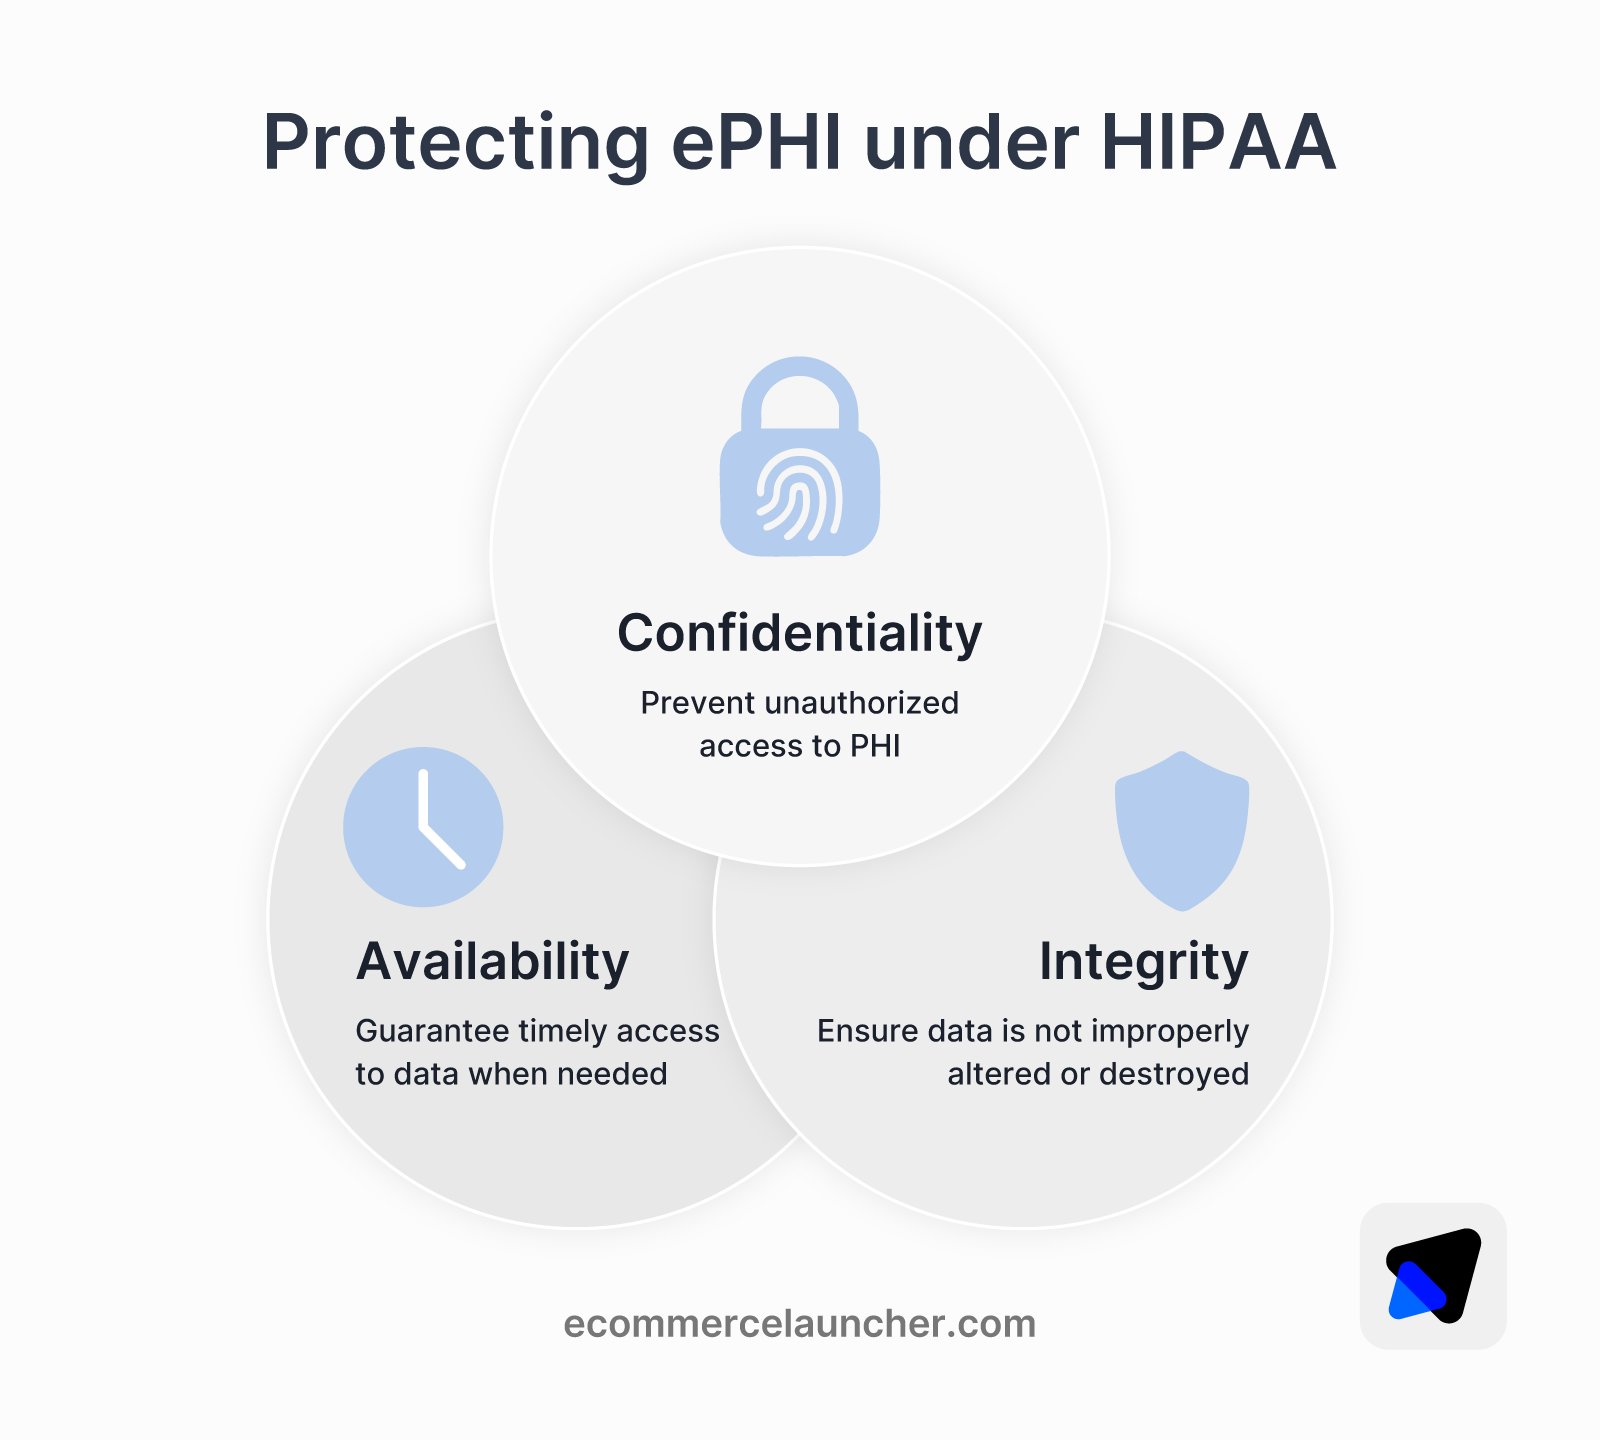
Under the HIPAA Security Rule (45 CFR §164.312), every hosting environment handling ePHI must protect three core outcomes:
- Confidentiality: Prevent unauthorized access to PHI.
- Integrity: Ensure data is not improperly altered or destroyed.
- Availability: Guarantee timely access to data when needed.
HIPAA doesn’t dictate specific tools, but it does require outcomes. Your host must implement hardened technical infrastructure—designed not only to support audits, but to identify risks, maintain logs, and ensure operational resilience during incidents.
Let’s explore two of the most critical areas: encryption and monitoring.
How Encryption Standards Differ Among Providers
HIPAA requires data to be encrypted both at rest (when stored) and in transit (when being transmitted), where needed. But the rule doesn’t define how—which means it’s up to you to confirm your host is using strong, modern encryption standards.
Look for:
- AES-256 encryption for data at rest. This is the current gold standard used by federal agencies and is considered unbreakable with today’s technology.
- TLS 1.2 or higher for data in transit. Earlier SSL/TLS versions are outdated and insecure.
- Full-disk encryption on all storage devices, including backups and replicas.
- Hardware Security Modules for encryption key management, especially in enterprise-grade environments.
Some providers only encrypt in transit, or charge extra for at-rest encryption. That leaves data exposed if a server is compromised.
Best Practice: Confirm that encryption is applied by default—not optional—and ask for documentation showing their encryption protocols and key management approach.
What Logging, Access Control, and Monitoring Must Be in Place?
Under 45 CFR §164.312(b) and (c), HIPAA requires systems to:
- Record access events.
- Review activity.
- Trigger alerts when something unusual occurs.
That’s why your hosting provider must offer a complete audit trail—not just basic access logs.
An easy way to ensure this is to choose a hosting provider that offers:
- Comprehensive audit logs, including logins, file access, config changes, failed attempts, and privilege escalations.
- Time-stamped records tied to unique user IDs and IP addresses.
- Intrusion detection/prevention systems (IDS/IPS) that monitor for and block known attack patterns.
- Role-Based Access Control (RBAC) so each user only accesses what they need, no more.
- Multi-factor authentication for all admin access.
- Retention policies that store logs for 6+ years, as recommended by HIPAA for historical auditability.
A hosting provider that skimps on monitoring may leave you blind to breaches until it’s too late.
Best Practice: Ask to see an example log report or real-time monitoring dashboard. If logs are hard to access or alerts are delayed, that’s a security gap—not just a compliance risk.
The 6 Best HIPAA-Compliant Hosting Providers in 2026
Choosing the right HIPAA-compliant hosting provider is crucial for safeguarding ePHI, ensuring compliance, and maintaining operational efficiency.
Here are my top 6 picks for HIPAA-compliant hosting providers with their offerings, strengths, and suitability for various healthcare needs.
1. Liquid Web
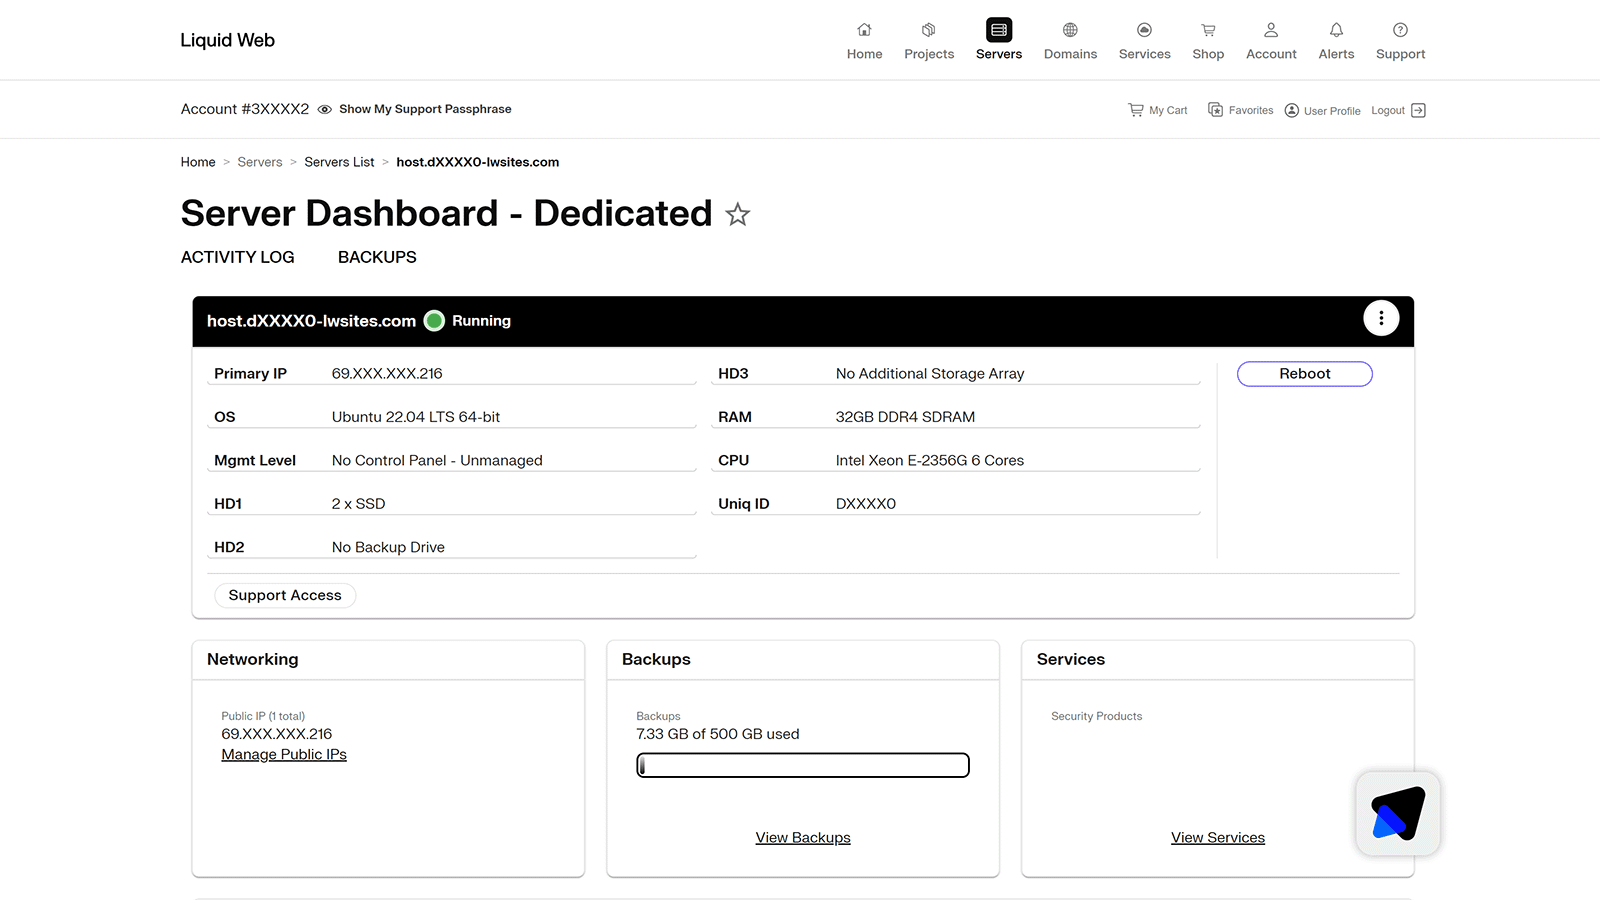
Liquid Web specializes in fully managed HIPAA-compliant hosting built for healthcare environments where failure isn’t an option.
Their infrastructure is designed not just to pass audits, but to prevent breaches, support mission-critical applications, and scale securely as your data footprint grows.
Liquid Web has its own data centers. That’s why it’s able to ensure all its HIPAA servers are hardened with physical safeguards, 24/7 monitoring, full encryption, and rapid-response support teams who understand the urgency of healthcare uptime.
I’ve used Liquid Web’s Bare Metal Server and my experience with them was fantastic. Their server was fast and customer service outstanding. That’s why, Liquid Web is my go-to recommendation for high performance, high-availability enterprise hosting.
Key Features:
- Fully managed HIPAA-compliant dedicated servers.
- Secure, redundant data centers with 100% network and power uptime SLAs.
- Encrypted VPN, offsite backups, IDS/IPS, and firewall protection by default.
- SOC 2, SSAE-18, and PCI-ready infrastructure.
- 24/7/365 human support with a 59-second live response guarantee.
Who It’s Best For: Healthcare providers, SaaS platforms, or EHR vendors that need a hands-off, audit-ready hosting solution with guaranteed compliance. Especially valuable for mid-size teams who want expert infrastructure without hiring a full DevOps team.
Pricing: Liquid Web’s HIPAA-compliant hosting plans start at $600. Advanced configurations with multiple dedicated servers are available, with pricing varying based on specific requirements.
Explore Liquid Web HIPAA Hosting
2. Convesio

Convesio offers a modern, HIPAA-compliant hosting solution designed to simplify meeting federal data protection standards for WordPress websites. Their platform runs on Docker-based containers, meaning every site is isolated for stronger security and better performance.
Convesio’s HIPAA hosting setup includes end-to-end encryption, offsite backups stored securely in Amazon S3, and detailed logging to help you pass audits and track access to sensitive data. Put simply, Convesio is one of the most secure WordPress hosting providers for ePHI.
Key Features:
- Containerized WordPress hosting for isolated, secure deployments.
- HIPAA-compliant encryption for data at rest and in transit.
- Daily offsite backups with Amazon S3 storage.
- Comprehensive audit logs and change tracking.
- Built-in Cloudflare Enterprise with WAF and DDoS protection.
- 24/7 access to Convesio’s team via Slack for real-time support.
Who It’s Best For: Ideal for healthcare practices, medical associations, and digital health teams running WordPress who need compliance without managing infrastructure. Especially useful for sites handling appointment bookings, telehealth content, or patient forms.
Pricing: Plans start at $150/month for HIPAA-compliant WordPress hosting. Higher tiers offer more storage, traffic capacity, and advanced support. All plans include core compliance features.
Explore Convesio HIPAA Hosting
3. Google Cloud Platform (GCP)
Google Cloud Platform is a powerful hosting option for healthcare providers that need to meet HIPAA rules in the U.S. It offers secure, fast, and flexible cloud services that can handle everything from storing patient data to running full healthcare applications. Ideal for headless websites and online stores.
Google signs a Business Associate Agreement and provides tools to help you build systems that protect health data. You’re in control of how your apps and files are set up, but GCP gives you a secure foundation to meet HIPAA requirements easily.
Key Features:
- Signed BAA.
- Default data encryption for storage and transmission.
- Identity and Access Management (IAM) tools.
- Cloud Audit Logs and Security Command Center.
- Meets ISO 27001, SOC 2, and other major compliance standards.
Who It’s Best For: Great for healthcare organizations, startups, or EHR developers that want full control over their apps while still meeting HIPAA rules. Best suited for teams with cloud or DevOps experience.
Pricing: GCP uses a pay-as-you-go pricing model. You only pay for what you use, which can help control costs as your needs change.
Explore Google Cloud HIPAA Hosting
4. Atlantic.Net
Atlantic.Net specializes in HIPAA-compliant hosting solutions, offering fully managed services tailored for healthcare providers. Their offerings include secure cloud and dedicated hosting environments, with a focus on compliance and data protection.
Atlantic.Net has been securing ePHI for over 30 years and brings a deep understanding of what real-world compliance takes. Every HIPAA hosting plan is backed by formal audits, a signed BAA, and a full security stack to keep your data safe.
Key Features:
- Fully managed HIPAA and HITECH-compliant hosting.
- BAA included, along with SOC 2, SOC 3 certifications.
- 100% uptime SLA with secure, redundant data centers.
- AES-256 encryption at rest and TLS 1.2+ in transit.
- Firewall, VPN, intrusion prevention, and malware protection included.
- Daily encrypted backups with optional disaster recovery add-ons.
Who It’s Best For: Medical practices, telehealth platforms, and EHR vendors that need secure hosting with minimal overhead.
Pricing: Plans start at $320.98 per month, with various tiers available based on specific needs and resources.
Explore Atlantic.Net HIPAA Hosting
5. Amazon Web Services (AWS)
AWS gives healthcare organizations huge flexibility, but with that power comes responsibility. Their cloud platform includes the tools you need to meet HIPAA rules, but you’ll need to set things up the right way because they follow a shared responsibility model.
What makes AWS a strong choice is how much is already in place: encryption, access controls, detailed logs, and a BAA that covers many core services. You choose the services you need—storage, databases, servers—and build your environment on top of a secure foundation.
That approach works well for teams that want control and already know their way around cloud services. If that’s you, AWS gives you scale, speed, and global reach—with built-in compliance support.
Key Features:
- Signed BAA covering many core AWS services.
- Encryption at rest and in transit using industry standards (AES-256, TLS 1.2+).
- IAM tools to control user access and limit permissions.
- Logging and monitoring through AWS CloudTrail and Config.
- Compliance-ready infrastructure with ISO 27001, SOC 2, and more.
Who It’s Best For: Best suited for healthcare IT teams, EHR vendors, or startups with in-house cloud skills. AWS gives you full control—but that means you’re responsible for maintaining HIPAA compliance within your own setup.
Pricing: AWS uses a pay-as-you-go pricing model. You pay for what you use, making it flexible for everything from small pilots to large deployments.
6. HIPAA Vault
HIPAA Vault is built for one purpose: keeping healthcare data safe and compliant. Unlike general-purpose hosting providers, every part of their service is focused on meeting HIPAA rules—from how your data is stored and backed up to how access is tracked and audited.
HIPAA Vault offers managed hosting for WordPress, Linux, and Windows environments, all with HIPAA security built in. What sets them apart is how much they handle for you: security updates, monitoring, backups, and compliance paperwork.
If you’re tired of patching together HIPAA support from multiple vendors, HIPAA Vault gives you one solution that covers everything.
Key Features:
- Fully managed HIPAA hosting with 24/7 security and support.
- Encrypted data at rest and in transit, by default.
- Signed BAA with every plan.
- Daily backups, malware scanning, and regular system updates.
- Real-time monitoring and audit logs for compliance tracking.
- Hosting options for WordPress, WooCommerce, Linux, and Windows servers.
Who It’s Best For: Ideal for clinics, health tech startups, or digital health agencies that want peace of mind.
Pricing: Plans start at $120/month for managed HIPAA WordPress hosting. Dedicated server options range from $299 to $599/month, depending on resources and setup.
Explore HIPAA Vault Hosting Solutions
Pricing Models and Value: What Are You Really Paying For?
HIPAA-compliant hosting isn’t just more expensive because of security—it’s more expensive because of accountability.
You’re not just paying for space on a server. You’re paying for the guarantee that your provider will meet federal data protection laws, respond fast during an incident, and help you survive a compliance audit. This is where many healthcare organizations get burned.
They start with a low-cost VPS or general cloud host, then scramble to add encryption, monitoring, backups, and a Business Associate Agreement—often finding those “extras” cost more than a properly bundled HIPAA solution from the start.
Let’s break down how HIPAA hosting is priced, and where you should spend vs. save.
Monthly vs. Annual HIPAA Hosting Costs
Most serious providers offer both monthly and annual pricing. Monthly is useful for early-stage projects or proof-of-concept builds. Annual plans typically come with price breaks and better support priority.
Here’s a general overview of pricing tiers:
| Tier | Use Case | Typical Price Range |
|---|---|---|
| Entry | Small site, WordPress portal | $120–$300/month |
| Mid-Level | EHR system, telehealth apps | $300–$700/month |
| Enterprise | Multi-region, HA infrastructure | $700–$1500+/month |
- Liquid Web offers fully managed HIPAA hosting starting around $600. That includes the BAA, security hardening, backups, and 24/7 expert support—so you’re not adding on hidden costs later.
- Convesio, focused on HIPAA-compliant WordPress, starts at $150/month, with pricing scaling based on traffic and backup needs.
- Google Cloud is usage-based—you pay for what you consume. That’s flexible, but also unpredictable if you’re unsure how much compute or storage your application will need long-term.
Takeaway: Flat-rate providers like Liquid Web offer simplicity and predictability, while platforms like GCP reward teams with cloud management skills.
Features That Impact Cost Most
Several key features affect pricing—some obvious, others not:
- The BAA: Providers like Liquid Web and HIPAA Vault include this by default. Some “HIPAA-ready” cloud platforms (like AWS or GCP) require you to opt in, or may limit which services are covered under their BAA.
- Security Management: Look for what’s included. Liquid Web bundles IDS/IPS, encrypted VPN, secure backups, and firewall management. On DIY platforms like Google Cloud, you’re responsible for adding and configuring these layers yourself.
- Support Quality: True HIPAA hosting means more than a ticket queue. Liquid Web guarantees a 59-second live response from support—critical when systems go down. Convesio also offers Slack-based support for real-time help. GCP support is tiered and costs extra.
- Disaster Recovery (DR): DR is a HIPAA expectation. Most managed HIPAA providers now include daily encrypted backups and defined RTO (Recovery Time Objective) and RPO (Recovery Point Objective) targets. Verify if they’re included or extra.
- Customization & Automation: Google Cloud offers flexibility—autoscaling, container orchestration, multi-region failover—but that requires in-house cloud architecture expertise. Liquid Web trades flexibility for managed reliability: they configure and maintain the stack so your team doesn’t have to.
Takeaway: If your team lacks cloud engineers, managed providers like Liquid Web are more cost-effective long term—even if their price looks higher upfront.
Case Studies: Healthcare Organizations Using HIPAA Hosting Successfully
Real-world results help separate marketing promises from proven value. Below are two examples of healthcare organizations that made the switch to HIPAA-compliant hosting and saw immediate improvements in security, operations, and patient outcomes.
Case Study 1: Specialist Pharmacy Transforms Patient Care with Liquid Web
The Challenge:
Specialist Pharmacy serves patients with rare conditions who rely on fast access to life-saving medications. But their old web host didn’t support HIPAA compliance, which meant no secure online forms—and patients had to mail in documents. That led to delays, frustration, and serious risks for patient health.
The Solution:
Specialist Pharmacy migrated to Liquid Web’s HIPAA-compliant hosting, powered by a VMware Private Cloud. With secure online forms, encrypted infrastructure, and dedicated support, they could finally collect sensitive health data safely and in real time.
The Outcome:
- Prescription refills that used to take weeks now happen in hours.
- 99% positive feedback from patients using the new online system.
- Hundreds of hours saved annually by automating refill requests.
- A dependable support team available whenever issues come up.
Customer Testimonial:
“Thanks to Liquid Web, we can engage with the patients more quickly and get them their medicine more quickly… sometimes up to three weeks faster.” — Director of IT Innovation, Specialist Pharmacy.
Lesson: The right hosting doesn’t just protect data—it directly improves patient health and staff efficiency.
Case Study 2: HIPAA Vault Supports Marketing Firm with Bulletproof Compliance
The Challenge:
Intrepy Healthcare, a medical marketing agency, was helping clients grow—but new HIPAA rules around tracking, cookies, and data privacy made their old host (WP Engine) a liability. They needed a hosting partner who could handle compliance without limiting marketing creativity.
The Solution:
Intrepy Healthcare partnered with HIPAA Vault to move all healthcare websites to HIPAA-compliant WordPress hosting. The platform came with encryption, monitoring, and expert support—all fully managed.
The Outcome:
- Full alignment with new data tracking rules.
- No compliance headaches—just secure, high-performing websites.
- Greater confidence during audits and client onboarding.
Customer Testimonial:
“What I love most about working with HIPAA Vault is their white-glove approach. They take a huge weight off our shoulders.” — Justin Knott, CEO, Intrepy Healthcare.
Lesson: Even non-clinical healthcare partners like marketers need HIPAA-compliant hosting when handling patient-related data.
HIPAA Hosting Provider Evaluation Checklist
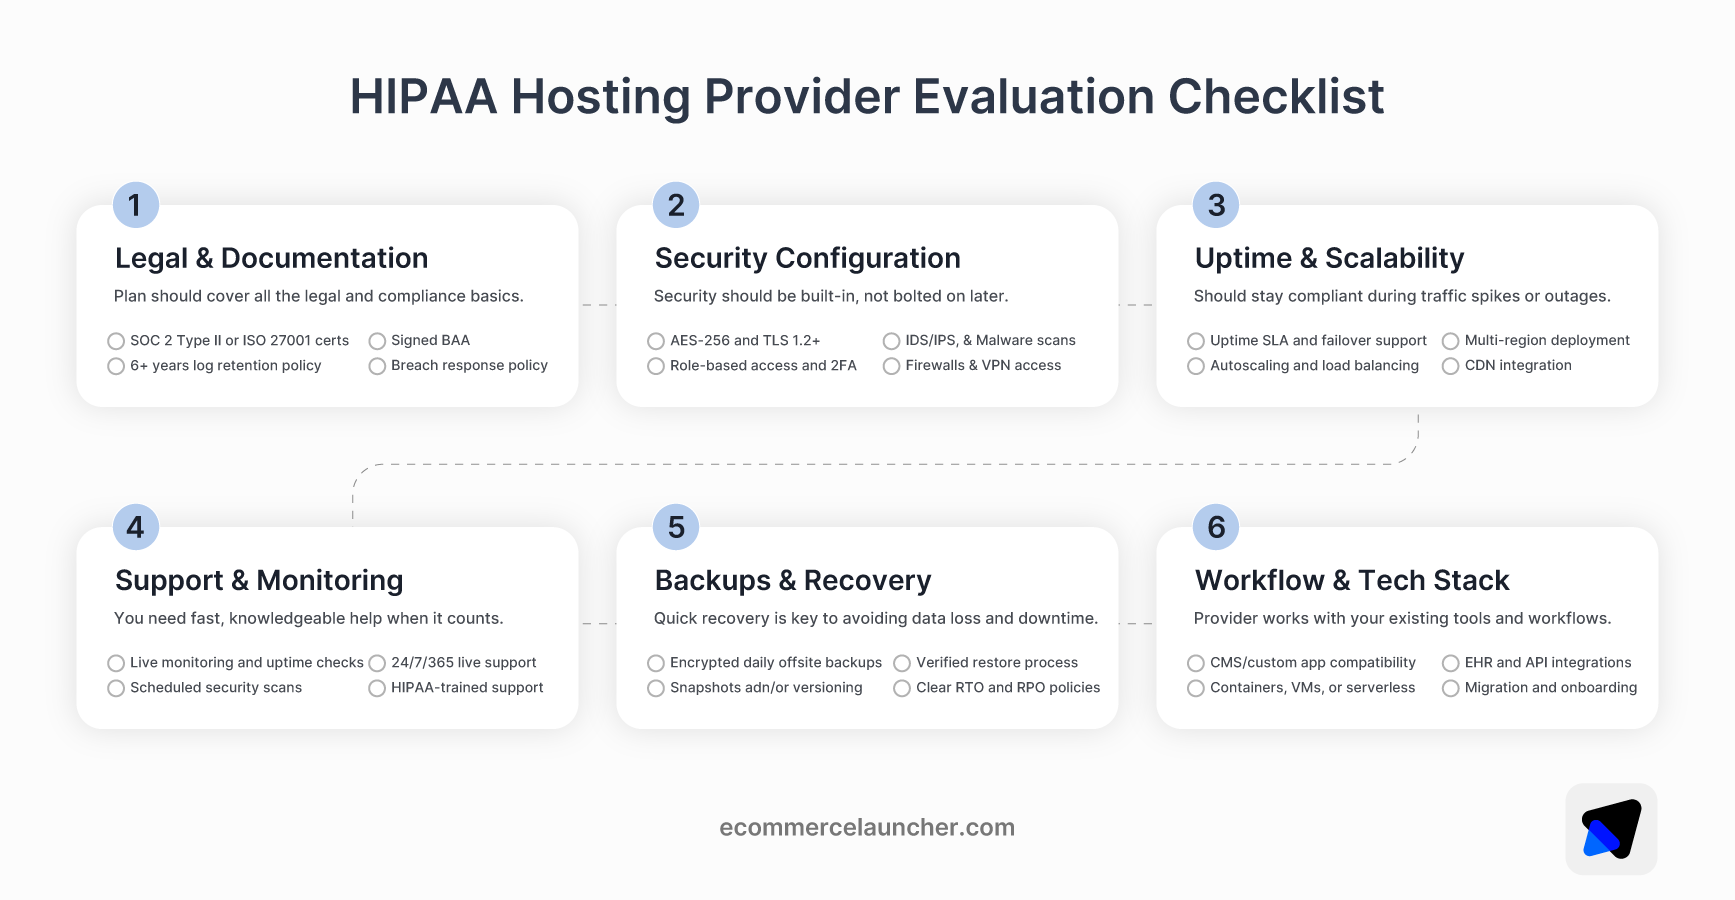
Choosing a HIPAA hosting provider is about protecting your patients, your business, and your reputation.
The following HIPAA hosting evaluation checklist breaks down the six core areas you need to evaluate: legal readiness, security, support, recovery, and infrastructure fit. Use it to compare providers and spot gaps before you choose one.
1. Legal and Documentation Readiness
Without the right paperwork and audit trail, your infrastructure isn’t HIPAA-compliant—no matter how secure it feels.
Look for:
- A signed Business Associate Agreement included in your plan.
- Clear explanation of which services the BAA covers.
- Documented incident response and breach notification timelines.
- Access to SOC 2 Type II or ISO 27001 certifications.
- Log retention policy of 6+ years.
Liquid Web includes signed BAAs, certified infrastructure, and compliance support upfront—saving you legal stress down the line.
2. Security Features and Configuration
HIPAA violations often come down to poor configurations. You need hosting that bakes in security by default—not as an afterthought.
Look for:
- Full encryption at rest (AES-256) and in transit (TLS 1.2+).
- IDS/IPS systems to detect and block intrusions.
- Daily or real-time malware scans.
- Managed firewalls and secure VPN access.
- Role-based access and two-factor authentication.
Convesio offers WordPress HIPAA hosting with built-in security hardening and Cloudflare Enterprise protection—ideal for teams that need strong defaults and quick launches.
3. Uptime, Scalability, and Traffic Readiness
Can your host handle a sudden spike in traffic—or a data center failure—without breaking compliance?
Look for:
- 100% uptime SLA or multi-zone failover support.
- Autoscaling and load balancing for high-traffic periods.
- Multi-region deployment options (especially if you serve patients nationally).
- CDN integration for faster global delivery.
Google Cloud provides auto-scaling, global failover, and container orchestration—best for teams with in-house cloud skills. For managed performance without the DIY setup, Liquid Web is an excellent choice.
4. Support and Monitoring
Delayed response times aren’t just inconvenient—they can be dangerous. That’s why you need access to real people who understand HIPAA.
Look for:
- 24/7/365 human support with fast escalation.
- Real-time monitoring and uptime dashboards.
- Regular vulnerability scans.
- Support staff familiar with HIPAA compliance.
Liquid Web’s 59-second support consistently ranks among the best in managed hosting.
5. Backup, Restore, and Disaster Recovery
If you lose data or access, how fast can your provider get you back online—without data loss?
Look for:
- Encrypted daily backups stored offsite.
- Verified restore process with recent test logs.
- Clear RTO/RPO policies that meet your needs.
- Options for versioning, snapshots, or multi-region DR.
Both Convesio and Liquid Web include managed backups in their HIPAA plans—so you don’t need to add third-party tools or scripts.
6. Fit for Your Workflow and Tech Stack
HIPAA compliance means nothing if the platform doesn’t support your real needs—like your CMS, APIs, or DevOps workflows.
Look for:
- Compatibility with your CMS (e.g. WordPress, Drupal) or custom apps.
- EHR and third-party API integration support.
- Support for containers, VMs, or serverless (depending on your build).
- Migration help or managed onboarding.
Convesio offers HIPAA-compliant WordPress hosting with isolated Docker containers and built-in security features, streamlining deployment for healthcare teams.
Google Cloud Platform offers extensive control and flexibility, ideal for teams with cloud expertise to configure and manage HIPAA-compliant environments.
Liquid Web combines flexible infrastructure with fully managed HIPAA-compliant hosting, perfect for supporting the rapid growth of healthcare applications.
Final Thoughts: You’ve Done the Research—Now Make It Count
You’ve seen what real HIPAA hosting should look like: strong encryption, airtight documentation, responsive support, and infrastructure that adapts when healthcare demands spike.
Now it’s about action.
Whether you need to support thousands of patient logins or just need to stop worrying about compliance errors, your next move should be a host that’s built for healthcare from the ground up.
You’re not just choosing a server—you’re choosing a partner who’ll be there when audit season hits, when traffic surges, and when timely access to care depends on uptime.
Start with a trusted HIPAA host like Liquid Web, or explore HIPAA WordPress Hosting by Convesio.
Have questions or need more help? Get in touch with me using our contact form.
